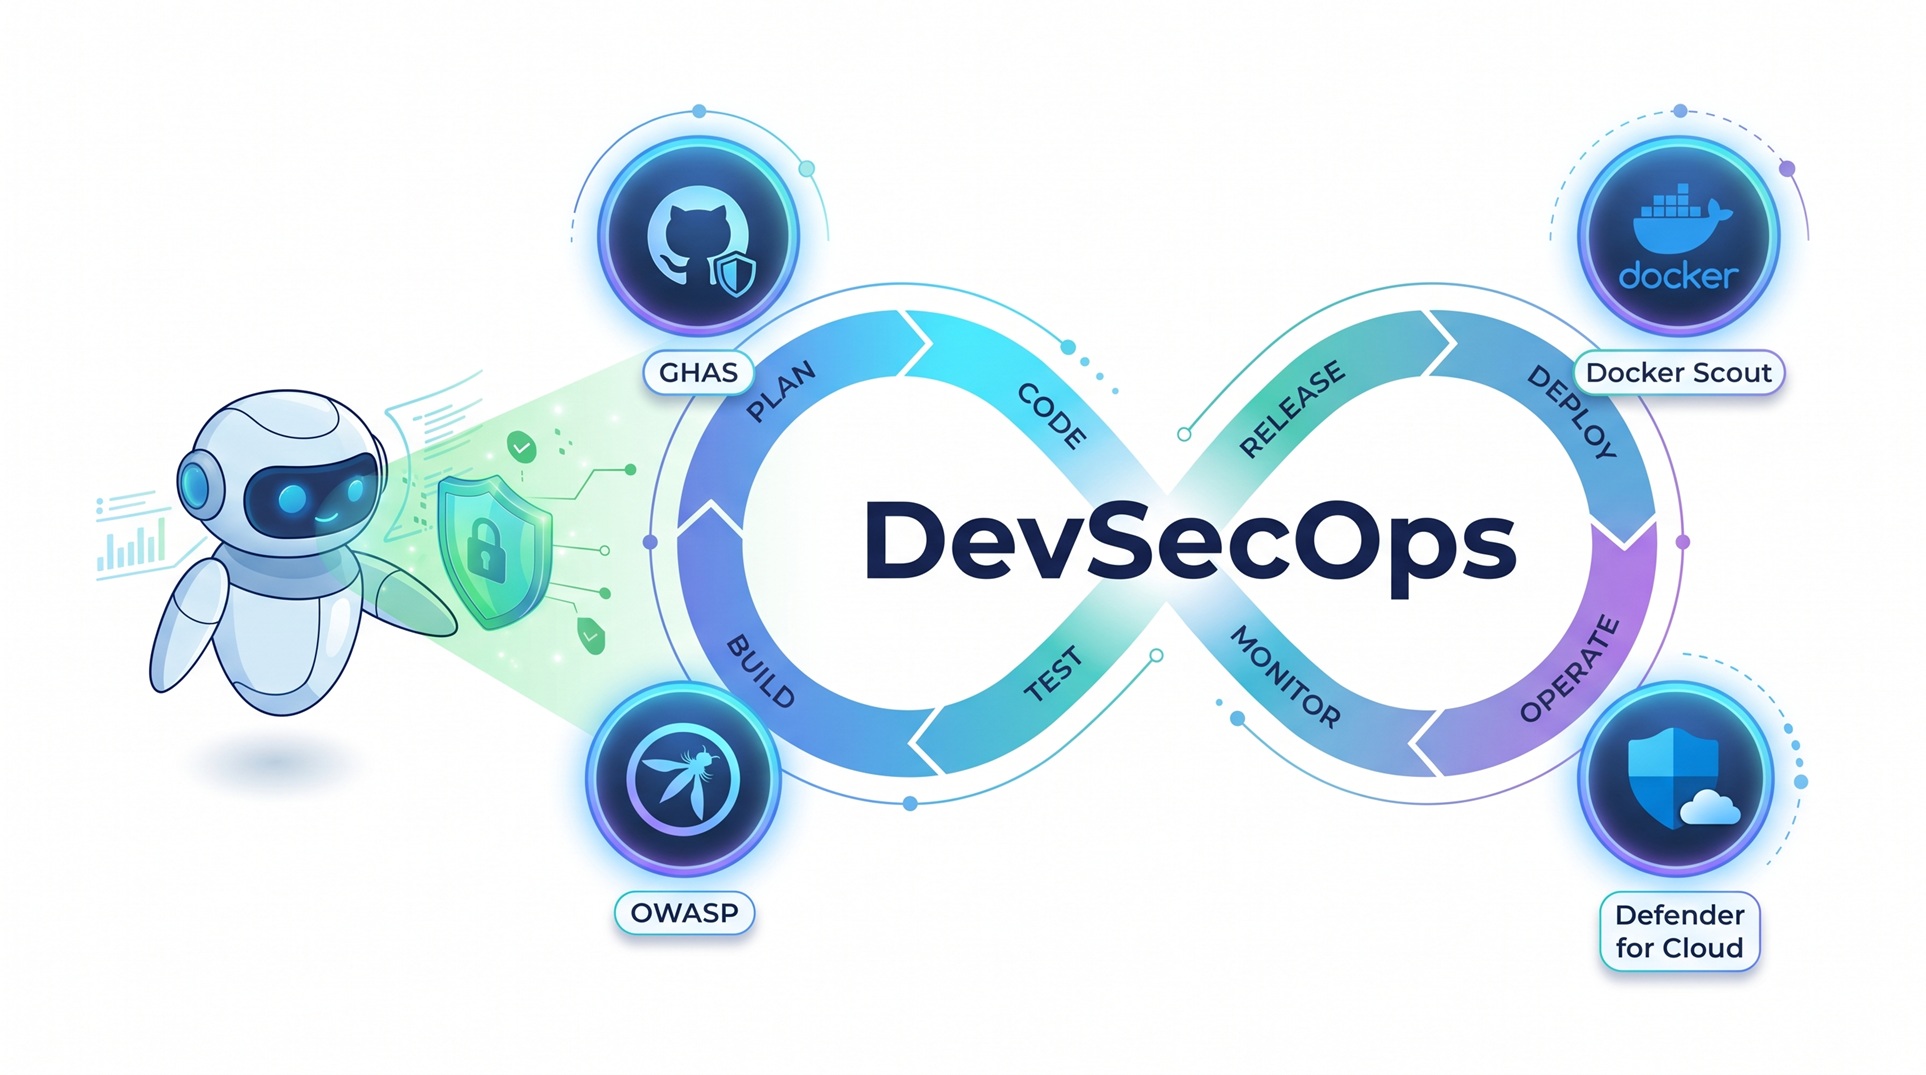
Closing the DevSecOps Gaps in the Agentic AI Era
· 17 min read
An AI agent updates an API, adds a dependency, and rebuilds its container. Code scanning passes. The image has no blocking vulnerability findings. The deployment succeeds.
That does not tell you whether one customer can read another customer's records, whether the build runner exposed a credential, or whether the deployed agent can be persuaded to misuse an authorized tool.
The security gap is not necessarily a missing scanner. It is often a missing connection between a risk, a control, evidence, and someone responsible for acting on it.